Google Gemini as a Workplace Agent: Governance First
The Problem: AI Tools That Act Are Already at the Door
Most businesses are still using AI as a sophisticated search engine — ask a question, get an answer, move on. That era is ending. The tools arriving now do not wait for a prompt. They take action inside your systems, on your behalf, without someone supervising every step.
Google Cloud's launch of Gemini as a fully autonomous workplace agent is the clearest signal yet (Reuters, 2026). This is not a chatbot bolted onto a search bar. It is designed to sit inside the tools your teams already use — email, CRM, document editors — and handle tasks end-to-end. The same pattern is playing out across Microsoft, Anthropic and a growing list of challengers.
For business operators, the problem is not whether these tools will reach them. It is whether they will be ready when they do. Most are not. The consequences of being caught unprepared are already visible.
Agents acting without defined approval boundaries can execute tasks that are difficult or impossible to reverse.
Staff are adopting consumer-grade AI tools informally, creating ungoverned data flows outside IT visibility (Bender et al., 2021).
Productivity gains go to the organisations that deploy first — those that hesitate fall behind on cost and speed.
Compliance exposure grows when AI touches regulated data, such as client communications or financial records, without audit trails.
Leadership teams lack clear ownership of AI decisions, leaving governance as everyone's problem and no one's priority.
Root Causes: Why Businesses Are Not Ready
The gap between AI capability and organisational readiness is not a technology problem. It is a process and culture problem. Most businesses have spent the past two years evaluating AI tools rather than building the operational infrastructure to deploy them safely (Brynjolfsson & McAfee, 2023). Evaluation is easy. Deployment with controls is hard.
The result is a predictable bottleneck. The software is ready. The organisations are not. And the root causes run deeper than a missing policy document.
No defined ownership: Decisions about which AI tools can access which systems fall between IT, operations and the C-suite with no clear accountability.
Absent workflow controls: Businesses lack approval gates and escalation paths for AI-initiated actions, meaning agents either run unchecked or never get deployed at all.
Data hygiene debt: Autonomous agents are only as reliable as the data they act on. Most CRMs and inboxes contain incomplete, duplicated or outdated records that no one has cleaned because no one had to.
Risk aversion without a risk framework: Leaders are cautious about AI but lack a structured way to assess which tasks are low risk and which are not, so nothing moves.
What Leading Organisations Are Doing
The businesses making the most progress are not the ones with the largest technology budgets. They are the ones that treated governance as a product — something to be designed, tested and iterated — before they handed agents any real authority (Reuters, 2026). They started narrow and expanded deliberately.
Across sectors from property and professional services to logistics and financial services, a consistent pattern is emerging among early adopters who are getting results without chaos.
How Leading Organisations Deploy AI Agents
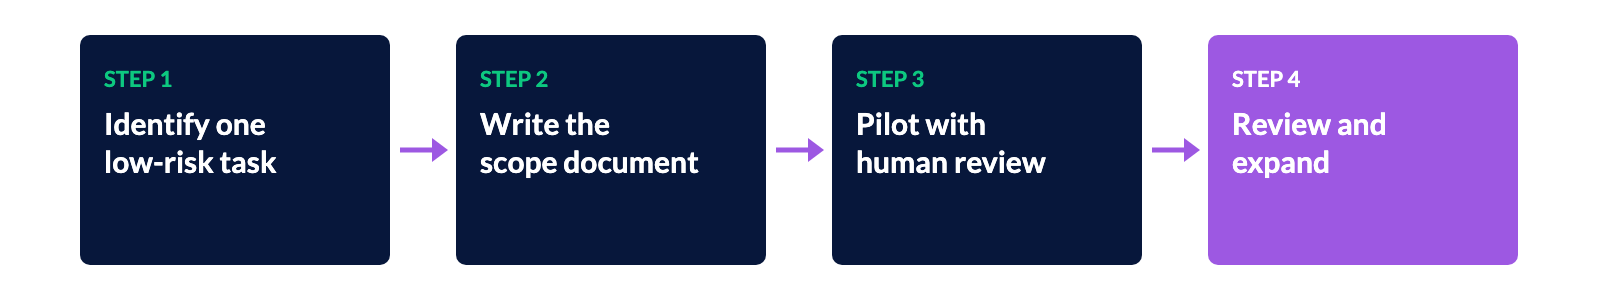
Starting with one low-risk task: A single, bounded workflow — such as drafting follow-up emails after client meetings — is used as the initial deployment, with human sign-off before anything sends.
Building audit trails from day one: Every AI-initiated action is logged with a timestamp, a rationale and the name of the human accountable for approving it.
Defining data access permissions explicitly: Agents are given read or write access only to the specific systems they need for a specific task — not broad access by default.
Running quarterly governance reviews: As agent scope expands, leading organisations schedule formal reviews to assess what the agent has done, what went wrong and what boundaries need updating.
The Core Solution: Governance-First Agent Deployment
The path to reliable AI agent deployment runs through governance, not capability. The question is not what the agent can do — it is what you have decided it is allowed to do, and how you will know if it does something else.
1. Define Task Boundaries Before Access Is Granted
Every agent deployment should start with a written scope document that specifies the tasks it can perform, the systems it can touch and the conditions under which a human must review its output before it takes effect (Brynjolfsson & McAfee, 2023).
List every action the agent will take — draft, send, log, flag — in plain language.
Assign a named human owner responsible for reviewing agent outputs during the pilot phase.
Set a hard limit on data access: the agent reads only what it needs for the defined task.
Document what the agent is explicitly not permitted to do, not just what it is permitted to do.
2. Build Approval Workflows Into the Process
Autonomous does not mean unsupervised at the start. The goal is to earn trust incrementally by demonstrating that the agent performs reliably within its defined scope before that scope expands (Bender et al., 2021).
Stage one: agent drafts, human approves before anything is sent or saved externally.
Stage two: agent acts, human reviews within a defined window and can reverse the action.
Stage three: agent acts autonomously on pre-approved task types only, with exception alerts for anything outside scope.
Log every stage transition with the rationale and the sign-off from senior leadership.
3. Measure and Audit Continuously
Governance is not a one-time exercise. Agent behaviour can drift as data changes, as integrations are updated or as staff interact with the agent in ways that were not anticipated at deployment.
Track error rate, escalation rate and reversal rate for every agent task category.
Review audit logs monthly during the first six months of any new deployment.
Survey the staff who work alongside the agent on accuracy, usefulness and unexpected behaviour.
Establish a clear process for pausing or rolling back agent access if error rates exceed a defined threshold.
Implementation Roadmap: A Practical Path Forward
Deploying an AI agent inside a live business system does not require a multi-year technology programme. It requires a structured sequence of decisions made before the software is switched on. The organisations that do this well treat the first deployment as a learning exercise, not a final answer.
Step 1 — Audit your current workflows: Identify three to five repetitive, time-consuming tasks that require minimal judgment and involve low-risk outputs. These are your candidate use cases for a first agent deployment.
Step 2 — Define the governance framework: For the top candidate task, write a one-page scope document covering permitted actions, data access, approval requirements and the human owner. Get sign-off from leadership before any tool is connected.
Step 3 — Run a controlled pilot: Deploy the agent on the defined task for four to six weeks with full human review of every output. Track accuracy, time saved and any unexpected behaviour.
Step 4 — Review and adjust: At the end of the pilot, assess the results against your defined metrics. Update the scope document, tighten or relax approval requirements based on evidence, and brief the team on what changes.
Step 5 — Expand deliberately: Add one new task or one new system integration per quarter. Repeat the pilot and review cycle for each addition. Do not expand scope based on enthusiasm — expand it based on data.
Key Takeaway
Google's move to deploy Gemini as a fully autonomous workplace agent is a signal, not an outlier (Reuters, 2026). Every major AI platform is moving in the same direction: from answering questions to taking action. The businesses that will gain the most from this shift are not the ones that adopt fastest — they are the ones that build the controls, ownership structures and audit processes that make autonomous action trustworthy. Capability is no longer the bottleneck. Governance is. That makes governance the most valuable thing you can build right now.
🚀 Ready to Deploy Agents Without the Risk?
AIVIA Systems works with business operators to design governance frameworks and pilot programmes for AI agent deployment — starting with a single workflow and building from there. If you are evaluating autonomous tools and want a structured path to deployment, we can help you move from evaluation to production without the guesswork.
Book a 30-minute governance readiness assessment to identify your lowest-risk first deployment candidate.
Request our AI agent scope document template to define task boundaries before any tool is connected to your systems.
Ask about our pilot design service, which covers approval workflows, audit logging and a review framework for your first six weeks.
Share this post with your operations lead or head of technology and start the governance conversation internally before the tools arrive.
Send your enquiries to [email protected] and a member of the AIVIA team will respond within one business day.
References
Reuters. (2026). Google Cloud introduces Gemini agent for work as AI race heats up. Reuters. https://www.reuters.com/business/google-cloud-introduces-gemini-agent-work-ai-race-heats-up-2026-10-08/
Bender, E. M., Gebru, T., McMillan-Major, A., & Shmitchell, S. (2021). On the dangers of stochastic parrots: Can language models be too big? Proceedings of the 2021 ACM Conference on Fairness, Accountability, and Transparency. https://dl.acm.org/doi/10.1145/3442188.3445922
Brynjolfsson, E., & McAfee, A. (2023). The productivity paradox of AI: Why capable tools need operational infrastructure. MIT Sloan Management Review. https://sloanreview.mit.edu/article/the-ai-productivity-paradox/
McKinsey & Company. (2024). The state of AI in 2024: Governance gaps and enterprise readiness. McKinsey Global Institute. https://www.mckinsey.com/capabilities/quantumblack/our-insights/the-state-of-ai
